Security and responsible AI, designed in from the first sprint
Identity, access, monitoring, AI red teaming and bias testing are part of the architecture of every solution.
What it does
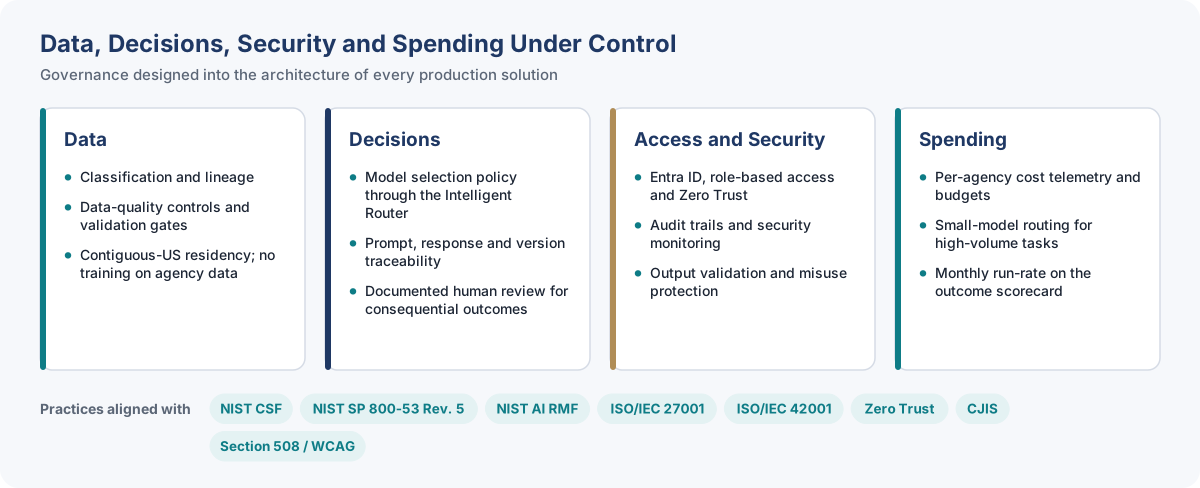
Production AI must give an agency clear visibility into the data being used, how outputs are generated, who can access the system and how outputs are validated. AlgebraIT builds those controls into the platform.
Security runs through the full lifecycle, from architecture and identity through development, testing, deployment, monitoring and ongoing operations.
Example solutions
The following six examples describe security and governance services.
- 01 Security and identity integration for AI and data systems
- 02 Zero Trust architecture and role-based access
- 03 AI red teaming for prompt injection, jailbreak and data leakage
- 04 Bias and fairness testing with documented findings
- 05 AI System Cards and decision traceability
- 06 Security monitoring with audit trails
How AlgebraIT delivers it
AlgebraIT holds ISO 9001, ISO/IEC 27001 and ISO/IEC 20000-1 certifications, as applicable to the certified scope. Delivery practices align with the frameworks below, selected according to the specific agency and system.
| Area | Technologies and methods |
|---|---|
| Security frameworks | NIST Cybersecurity Framework, NIST SP 800-53 Rev. 5, Zero Trust, CJIS |
| AI governance | NIST AI Risk Management Framework, ISO/IEC 42001 |
| Identity and monitoring | Microsoft Entra ID, role-based access control, security information and event management |
| Accessibility | Section 508 and WCAG |
Controls built in
The following four controls are standard.
- All client data, including prompts, outputs, logs and backups, stays in contiguous-US cloud regions
- No open critical or high security findings at release
- Prompt-injection and data-loss guardrails on every AI endpoint
- Immutable audit logs retained to the agency schedule
Review the controls for your use case
We map your security and AI policy requirements to the evidence the platform produces.